Menu
Defence, DTIB and sovereign sectors
Your accreditation file, prepared on-premises, without tying up your experts.
Security accreditation is a contractual obligation, renewed for every system and every site. Risk Hunter prepares the EBIOS RM analysis and the accreditation documents within your environment, fully air-gapped.
In production on-premises, air-gapped, at a defence and healthcare organisation.
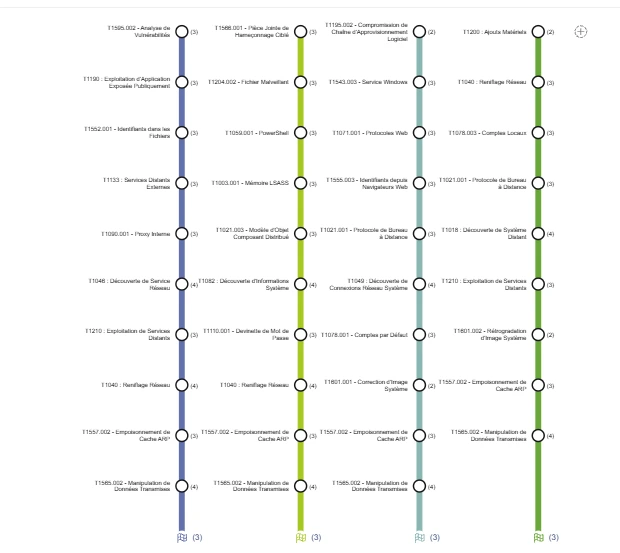
Operational scenario · example built on public data
Poorly segmented remote maintenance → supervision network → RTU gateways → man-in-the-middle on Modbus and IEC 60870 → falsified measurements.
Why defence is different
Three constraints that mainstream tools cannot meet.
Online compliance platforms and traditional GRC tools assume a CISO, an Internet connection and an external AI. The defence supply chain often has none of the three.
An obligation, not a project
No accreditation file, no go-live, no contract. And the file has to be redone for every new system, every new site, every renewal.
Experts you don’t have
Most companies in the supply chain have no dedicated CISO. The risk analysis falls to a part-time IT manager or a consultancy billed by the day.
Data that never leaves
Restricted information, air-gapped environments, cleared personnel: a tool that needs the Internet or an external AI is ruled out before the first demo.
Is your next accreditation coming up?
Prepare my fileWhat you get
The five EBIOS RM workshops, prepared. The file, ready for review.
One person launches the analysis from your documents and your exposure. Your experts step in to review, not to write.
- 1
Scope and security baseline
Scope, business assets and supporting assets, pre-filled from your documents and your systems’ exposure.
- 2
Risk origins and strategic scenarios
Risk origins, target objectives, paths through the ecosystem and stakeholders.
- 3
Operational scenarios
Attack paths detailed as MITRE ATT&CK techniques, blind spots included.
- 4
Risk treatment
Measures, residual risks, treatment plan submitted for approval.
- 5
The accreditation documents
Analysis, treatment plan and supporting evidence, ready for the accreditation authority. Your experts scope, adjust and approve.
Designed by auditors
Risk Hunter produces what an accreditation authority and an auditor expect: the structure, the rationale and the evidence, in the order they read them.
A clear offer for defence SMEs
One scope, one system, a first file: you get started without a dedicated CISO or a consultancy billed by the day, then extend to further systems on the same data.
See the five workshops prepared on a defence use case.
See a demoAfter accreditation, compliance
IGI 1300, II 901, ISO 27001, NIS2: actions driven by your data, not by spreadsheets.
Once accredited, the requirements keep coming. Risk Hunter assesses them against your data and turns every gap into an action tracked through to evidence.
Every requirement checked against your documents and data
IGI 1300 and II 901 (French instructions for classified and restricted information systems), your prime contractors’ requirements, ISO 27001, NIS2: proposed status, gap and source excerpt for every requirement, across the whole corpus rather than a sample.
Every gap becomes a managed action
Owner, deadline, cost, expected evidence. Prioritised by the risk it reduces and the regulatory deadline, linked to the requirement it covers.
A plan that updates when your data changes
A revised document, a new system, a newly disclosed vulnerability: the affected gaps and actions are recalculated, without redoing the file.
A compliance status the authority and the board can read
Compliance rate by framework and chapter, overdue actions, missing evidence: the same view serves for reporting and for decision-making.
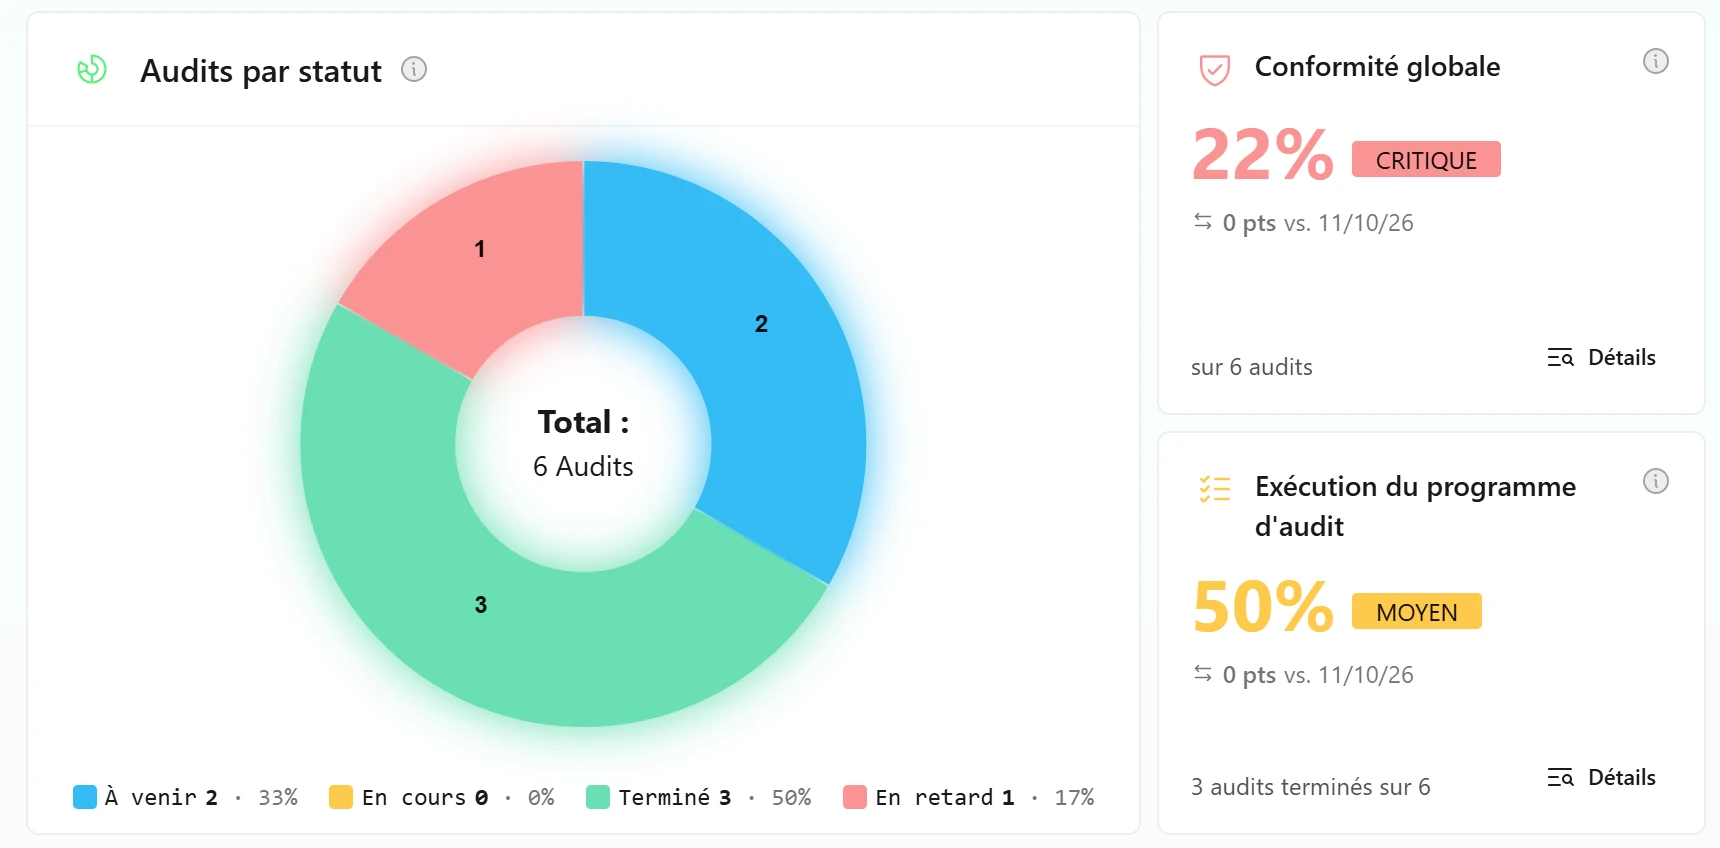
Your IGI 1300 and II 901 gaps, assessed in a demo.
Assess my complianceControl
Nothing leaves your perimeter.
Built for the most demanding environments, and already in production in one of them.
Within your environment
Installed on your servers, including in air-gapped environments, with no outbound connection.
The AI model of your choice, running locally
Mistral or your in-house model; a “European models only” configuration is available. No data is ever used to train a model.
Your prime contractors’ requirements
Contract security frameworks and clauses built into the analysis; every measure linked to the requirement it covers.
Consistent from one system to the next
Same criteria for every file: the accreditation authority finds the same structure, and you build on your work from one site to the next.
A demo in an air-gapped environment, on a defence use case.
Book my demoFAQ
Answers before you book.
Does it work without any Internet connection?
Yes. The air-gapped deployment is the one running in production at a defence and healthcare organisation.
Who approves the analysis?
Your experts, and only them. Risk Hunter prepares, cites its sources and records what was approved, by whom and when.
We don’t have a CISO. Is that a problem?
No. One person launches the analysis from your documents; our team can run the first file with you if you wish.
Is our data used to train a model?
Never. The model runs in your environment, and you choose it.
Your next accreditation file, prepared with Risk Hunter.
A demo on a defence use case, then a first file on your own scope, under an approved framework.