Skip to content
Risk Hunter, home
FRENBook a demo
Menu

AI platform for risk analysis and compliance

Your risk analyses and audits in 30 minutes*.

You rebuild every analysis and every audit by hand, for weeks, at every deadline. Risk Hunter industrialises them: EBIOS RM analyses, audit findings and action plans, every conclusion backed by its source. Your experts decide.

* Average observed across our customers, excluding review time.

See Risk Hunter on:auto-play, click to choose

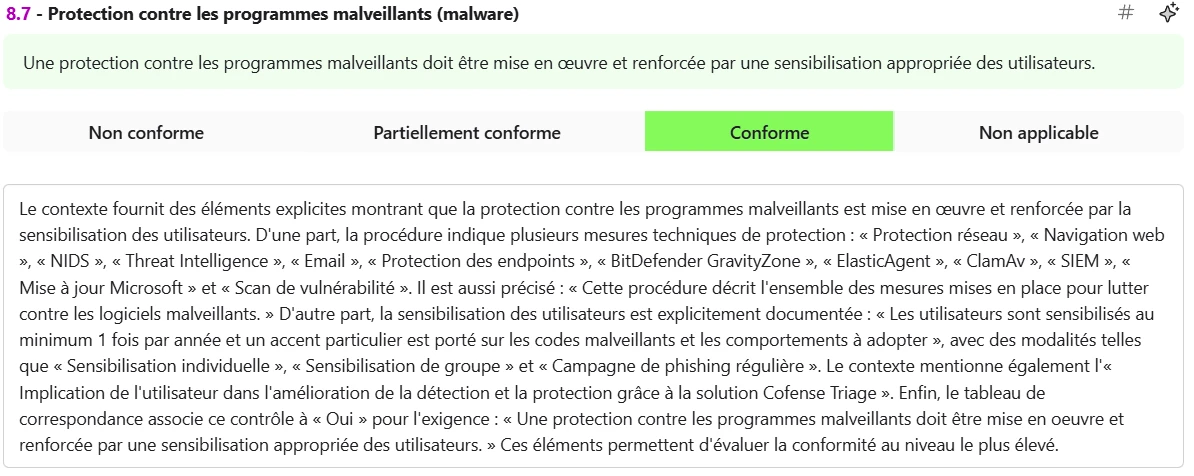
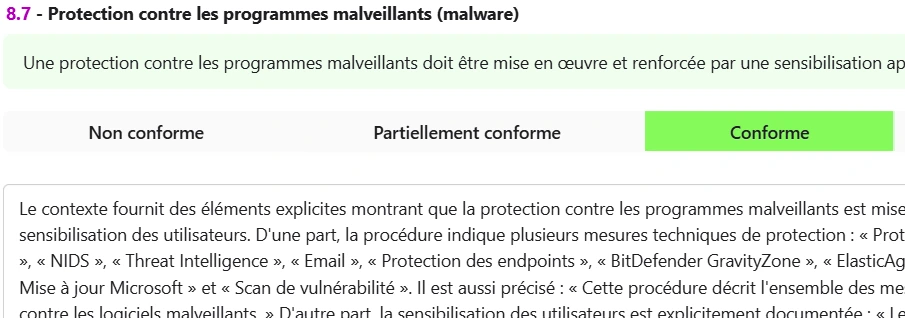
Actual Risk Hunter screen: ISO 27001 requirement 8.7 assessed as “Compliant”, with a rationale quoting passages from the organisation’s documents
  • The requirement from your framework, here ISO 27001.
  • The proposed status, which the auditor confirms or corrects.
  • The rationale, quoting the exact passages from your documents.
Actual Risk Hunter screen · Enlarge the full finding

Attack path · fictitious example

From a fake portal to encrypted servers

  1. T1566.002
    Spearphishing link
  2. T1539
    Steal web session cookie
  3. T1078.004
    Cloud accounts
  4. T1087.004
    Cloud account discovery
  5. T1133
    External remote services
  6. T1018
    Remote system discovery
  1. 1 · T1566.002
    Document management administrators receive a targeted email leading to a fake portal, an exact copy of the cloud platform.
  2. 2 · T1539
    The fake portal relays the login in real time and captures the session cookie: multi-factor authentication is bypassed.

… then 8 more steps through to encryption.

Exposure & remediation: every step of the attack mapped to its MITRE ATT&CK technique. Illustration, fictitious example.
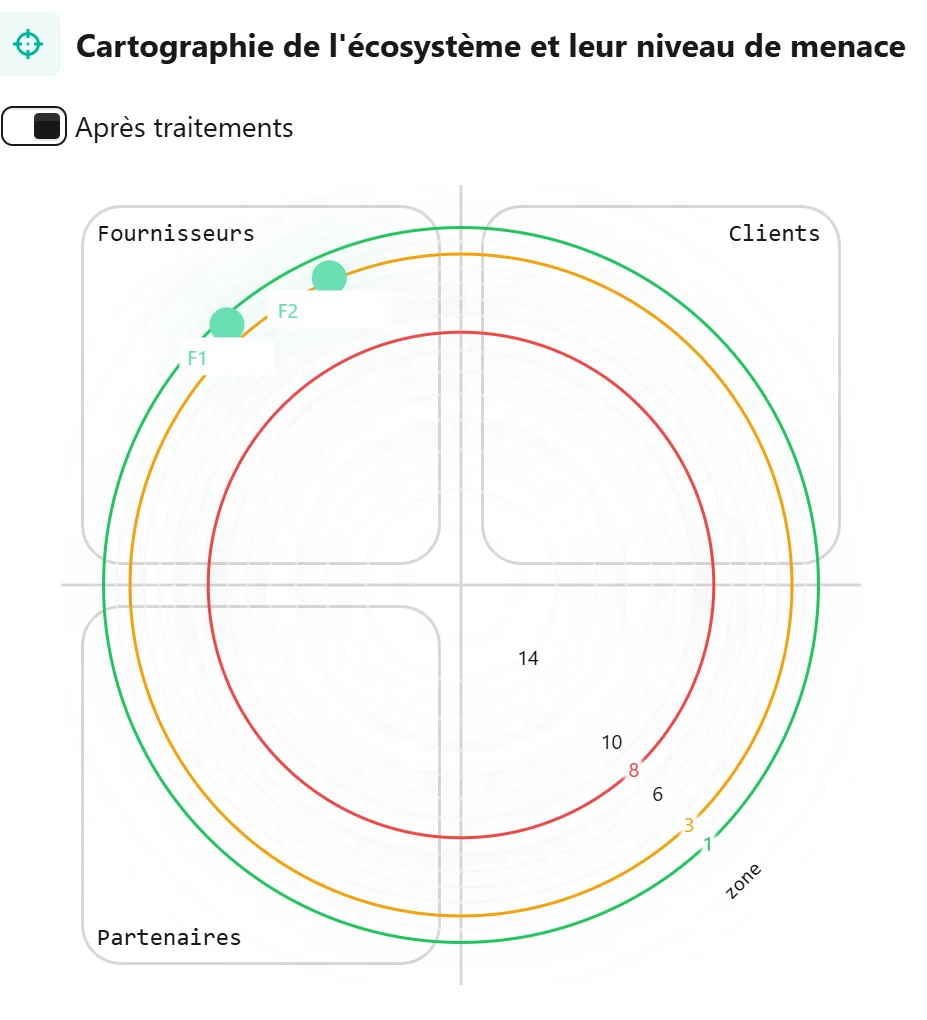
Actual Risk Hunter screen: ecosystem threat map, with suppliers, customers and partners positioned by threat level
Third parties & DORA: every supplier positioned by the threat it poses, before and after treatment. Actual screen.
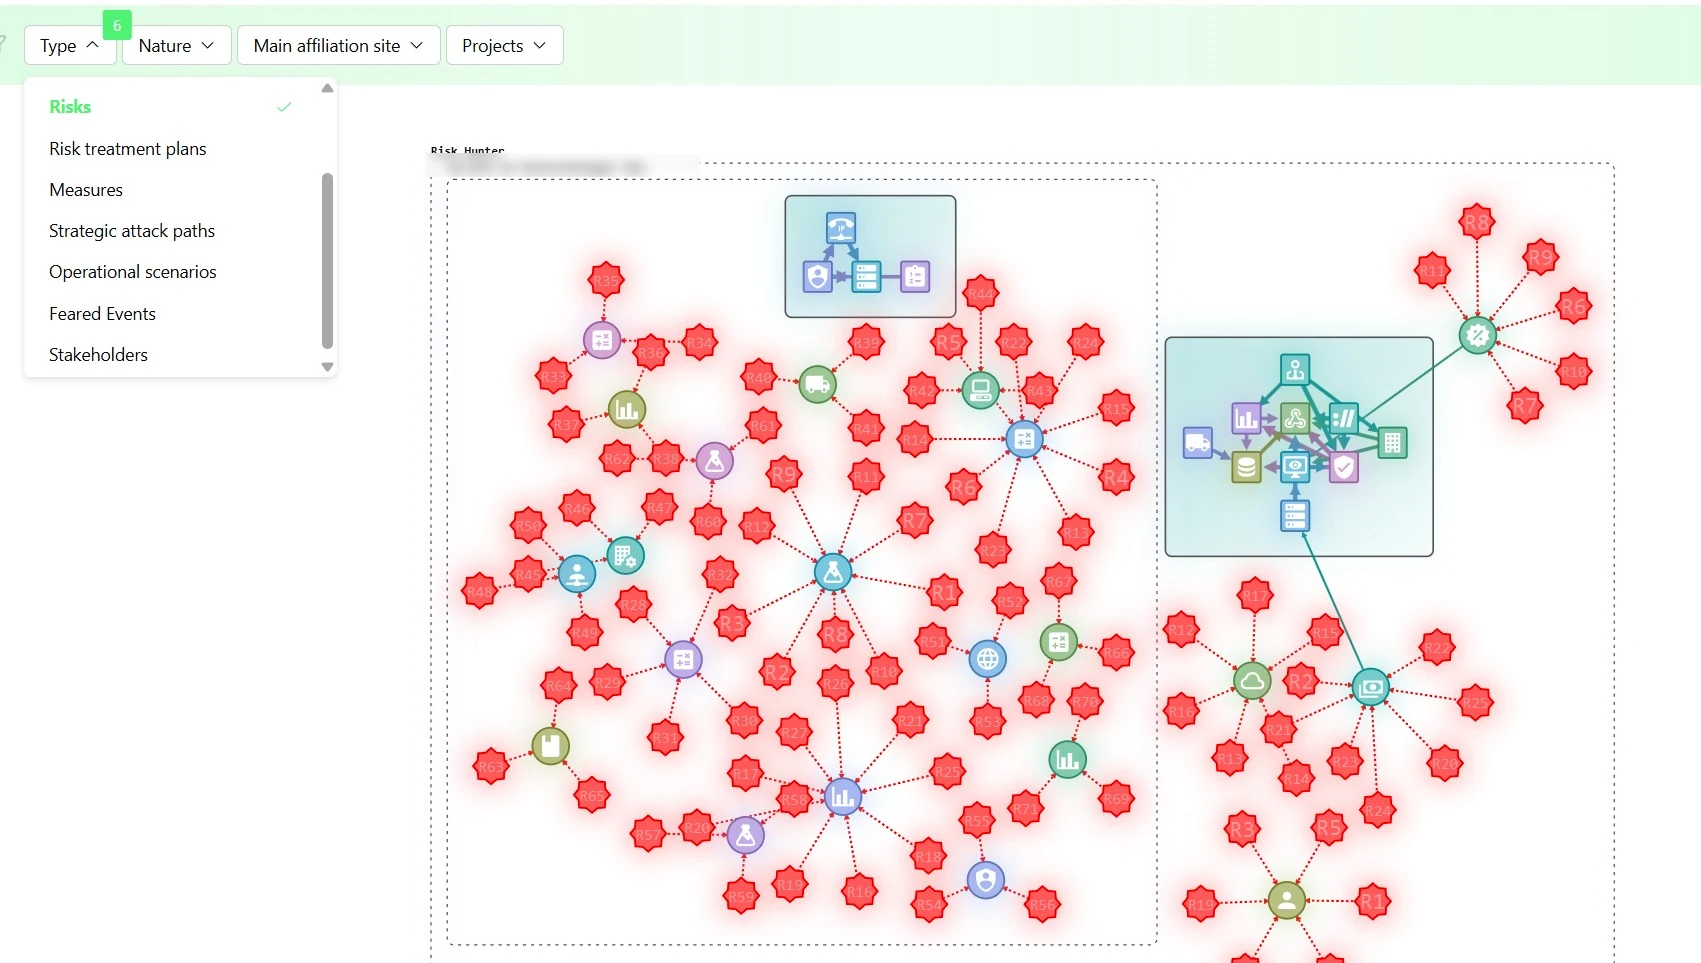
Actual Risk Hunter screen: risk graph linking assets, feared events and treatments
EBIOS RM accreditation: risks, assets and treatments linked together. Actual screen.

Three things your teams can no longer do on their own

Prove

Never be caught out on the day of the audit, the inspection or the accreditation. Every conclusion cites its source; everything approved is dated and attributed.

Produce

Analyses, findings and action plans ready for review, without tying up for weeks the experts you don’t have.

Stay in control

Data that never leaves your perimeter, on-premises and air-gapped if needed, and consistent results that don’t depend on a single person.

Use cases

For every deadline, a deliverable ready for review.

A critical vulnerability, an audit, a supplier, an accreditation: start from your situation, Risk Hunter prepares the file.

CISOs and security teams

Continuous exposure & remediation

MITRE ATT&CKMITRE ATLAS

New vulnerabilities arrive every day. You know which ones threaten a critical service, what to do, and by when.

You get

Justified priorities, remediation plan, evidence

Explore this use case

Compliance & audit

Audit & compliance

ISO 27001CRADORAHDSAI Act

An ISO 27001, NIS2, DORA or HDS audit is coming up. Every requirement is checked against all of your documents.

You get

Requirement-by-requirement pre-audit, gaps, action plan

Explore this use case

Procurement, third-party risk, DORA

Third parties & DORA

DORANIS2

A critical provider administers your systems. You measure the risk it puts on your business and what you need to require of it.

You get

Third-party scenario, measures, contractual requirements

Explore this use case

CISOs, accreditation authorities

EBIOS RM accreditation

EBIOS RMIGI 1300II 901

A system needs security accreditation. The risk analysis is pre-filled; your experts review and approve it.

You get

Complete EBIOS RM analysis, accreditation file

Explore this use case

Defence, DTIB and sovereign sectors

Your accreditation file, prepared on-premises, air-gapped, without tying up your experts.

Already in production in an air-gapped environment at a defence and healthcare organisation.

See the Defence & DTIB offer

What you get

Every decision deserves evidence.

Three deliverables, exactly as they appear in Risk Hunter. Every conclusion traces back to its source; nothing is binding without human approval.

Your documentsFindingExpert decisionEvidencepolicies, scans, contractsstatus, gap, excerptapproved, dateddefensible, versioned

Audit & compliance

Every requirement assessed, every conclusion sourced.

  1. 1

    You upload your documents

    Policies, procedures, BCPs, existing evidence.

  2. 2

    Risk Hunter assesses every requirement

    Proposed status and a rationale quoting the exact passages.

  3. 3

    The auditor checks and approves

    What was proposed and what was approved remain separate, dated and attributed.

ISO 27001 8.7 finding assessed as “Compliant”, with a rationale citing the organisation’s documents
Actual screen: full ISO 27001 findingEnlarge

EBIOS RM risk analysis

Detailed attack scenarios, technique by technique.

Attack path · fictitious example

From a fake portal to encrypted servers

  1. T1566.002
    Spearphishing link
  2. T1539
    Steal web session cookie
  3. T1078.004
    Cloud accounts
  4. T1087.004
    Cloud account discovery
  5. T1133
    External remote services
  6. T1018
    Remote system discovery
  1. 1 · T1566.002
    Document management administrators receive a targeted email leading to a fake portal, an exact copy of the cloud platform.
  2. 2 · T1539
    The fake portal relays the login in real time and captures the session cookie: multi-factor authentication is bypassed.

… then 8 more steps through to encryption.

Illustration of an attack path as Risk Hunter generates it, fictitious example.

Compliance management

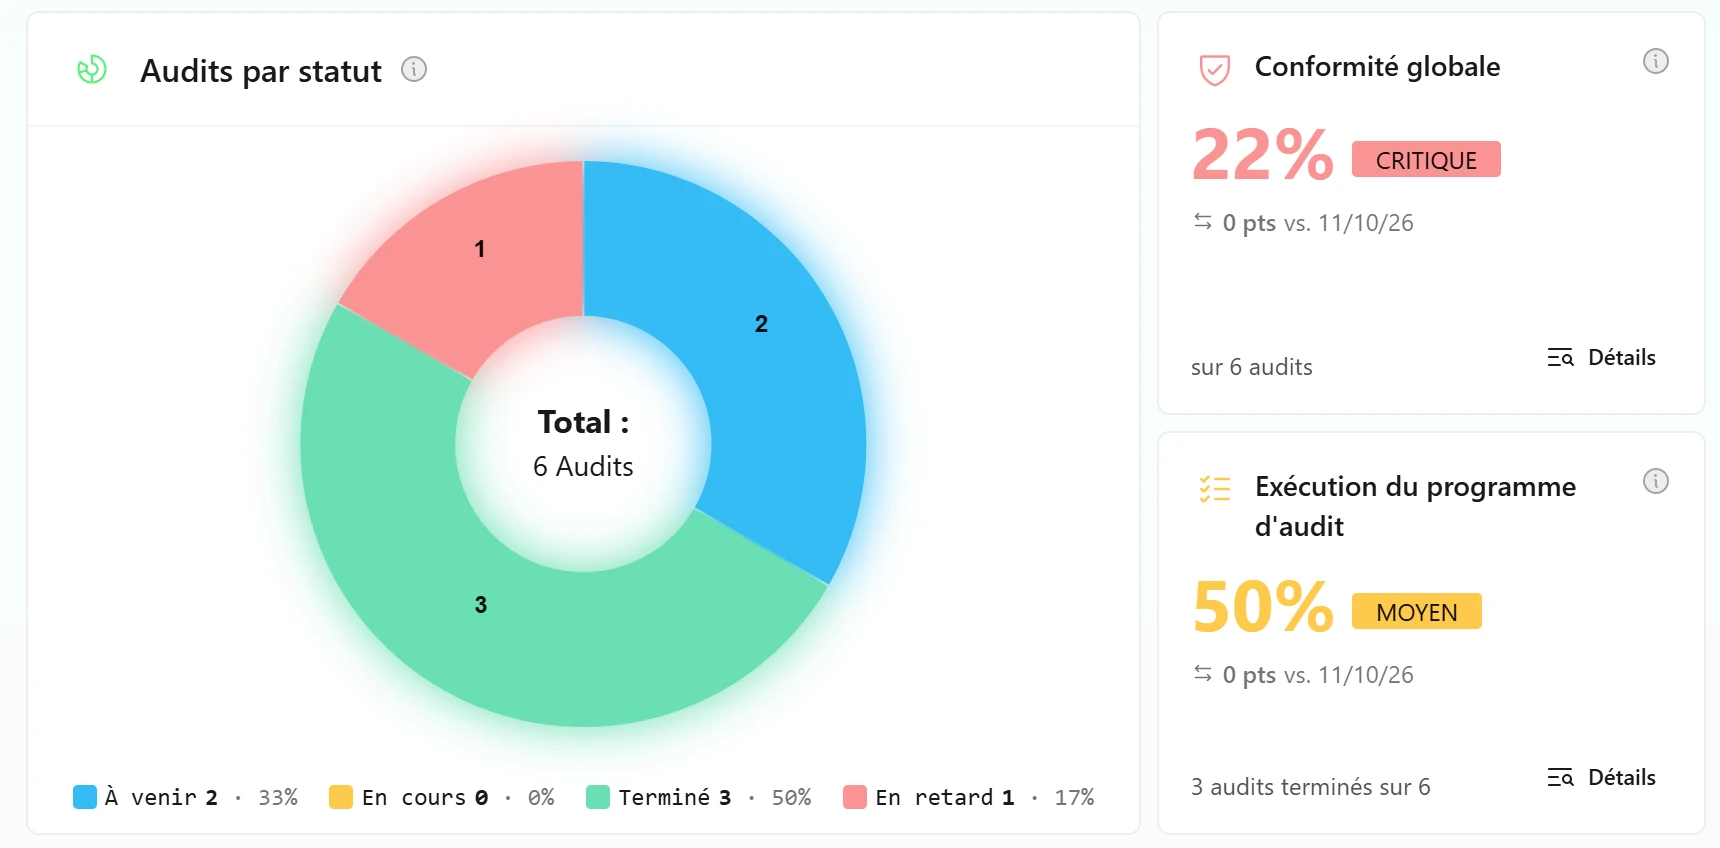
Your audit programme, tracked at a glance.

Risk Hunter dashboard: audits by status, overall compliance and audit programme execution
Actual screen: dashboard, demo dataEnlarge

Also available: document review (policy, BCP, DRP), internal control plan, costed action plan, executive report. Screens captured on demo data.

See these deliverables produced on a use case from your sector.

Book a demo

Time saved

Where audit time goes, and what Risk Hunter gives back.

With Risk Hunter, your experts only step in to review. The rest of their time goes back to the business.

A compliance audit

By hand
auditors and auditees
Framework
Evidence collection
Requirement-by-requirement analysis
Findings and gaps
Action plan
Review
With Risk Hunter
one auditor launches the audit
Generation
Auditor review
Time given back to your auditors
Time →

An EBIOS RM risk analysis

By hand
CISO, CIO, business teams, providers
Workshop 1
Workshop 2
Workshop 3
Workshop 4
Workshop 5
Review
With Risk Hunter
one person launches the analysis
Workshops 1 to 5
Expert review
Time given back to your teams
Time →

Up to 30 days → under 30 minutes*

For a risk analysis: weeks of workshops for a dozen scenarios by hand; a few minutes for hundreds with Risk Hunter.

Every requirement, every document

The audit covers all of your documents, not a sample read by hand.

Review stays with you

Your experts check and decide; the time saved on preparation goes to your other priorities.

* Average observed across our customers, excluding review time. Timeline proportions are illustrative.

How much time would you save on your next audit?

Estimate my savings in a demo

The demo

What Risk Hunter does, in three steps and three minutes.

One platform, whatever your starting point. The video shows it on a cyber exposure use case, using demo data.

Discover exposureLink to business riskTreat and prove

Assets, services, vulnerabilities and documents consolidated and mapped to your organisation and projects.

Engine: Native Exposure Collector

Every vulnerability and every gap linked to attack scenarios, blind spots and the impact on your operations.

Engine: Exposure-to-Risk

An action plan prioritised by risk reduction, approved by your experts, with time-stamped evidence for every decision.

Engine: Remediation Intelligence

Risk Hunter demo thumbnail: from vulnerability to remediation, in one platformWatch the demo · 3 min

This demo, on your own scope and frameworks.

Book my demo

Why Risk Hunter

Your files no longer get rebuilt by hand. They keep themselves up to date.

Move from slow manual work, redone at every deadline, to an analysis that evolves with your organisation.

A general-purpose AI

answers a question.

A traditional GRC tool

stores what your experts type in.

Risk Hunter

produces the deliverable, keeps it current and proves it.

Living, not frozen

No more rebuilding the file for every audit. When a document, a vulnerability or a supplier changes, the analysis and the gaps update continuously.

An auditable AI

On inspection day, you can show how every result was produced: the cited source, the method, the version, and who approved it.

Consistent deliverables

Same frameworks, same criteria, whatever the auditor or the entity: your results are comparable across subsidiaries and from one year to the next.

One data set, all your frameworks

ISO 27001, NIS2, DORA, HDS, accreditation: the same evidence requested five times, in five formats. With Risk Hunter, data qualified once serves every framework.

Your data finally works for you

Policies, scans, contracts, findings: what sat idle in files becomes risks, priorities and evidence, reused from one file to the next.

An AI pipeline designed and controlled by auditors: frameworks, methods and a library of attack scenarios built by auditors. The model is interchangeable; this expertise is not.

What your executive board sees

A critical vulnerability is not always a critical risk.

Operational scenario, fictitious example

A ransomware attack, told end to end

  1. 1The attacker spots a provider’s VPN portal exposed to the Internet.
  2. 2They get in with stolen credentials, as there is no multi-factor authentication.
  3. 3They pivot to the internal network through remote desktop: a blind spot.
  4. 4They exfiltrate customer data to their server.
  5. 5They encrypt the servers: billing stops.
High likelihoodEstimated impact ≈ €1.2M

The action that breaks the chain

Multi-factor authentication and segregated provider access: breaks steps 2 and 3.

MITRE ATT&CK: T1595 · T1078 · T1021 · T1041 · T1486

Strategic scenario, fictitious example

The attack that comes through your partner

  1. SourceAn organised cybercrime group seeking a ransom.
  2. Third partyYour managed service provider, which administers your servers remotely.
  3. PathThey compromise the provider, then use its legitimate access: a blind spot.
  4. ImpactBilling is down for several days.
High third-party threatCritical severity

Measures on the third party

Administration bastion, multi-factor authentication, right-to-audit clause: likelihood goes down.

MITRE ATT&CK: T1199

Fictitious examples; organisation and amounts are illustrative.

See the detailed comparison, criterion by criterion
A general-purpose AIA traditional GRC toolRisk Hunter
Who produces the analysisA general-purpose AIIt answers your questions, one at a timeA traditional GRC toolYour experts type it into the tool during workshopsRisk HunterRisk Hunter produces it; your experts approve it
From one run to the nextA general-purpose AIAn answer that can vary from one run to the nextA traditional GRC toolDepends on who enters the dataRisk HunterSame method, same criteria: a traceable, reproducible result
ConsistencyA general-purpose AIDepends on the prompt and context providedA traditional GRC toolVaries from one auditor or entity to anotherRisk HunterThe same framework applied everywhere, comparable over time
What it knows about youA general-purpose AIWhatever you paste into the chatA traditional GRC toolWhat was declared in workshopsRisk HunterYour assets, vulnerabilities, documents and suppliers, all linked
MethodA general-purpose AIDepends on the promptA traditional GRC toolThe method, applied by handRisk HunterEBIOS RM, ISO 27005, ISO 19011, applied by the software
EvidenceA general-purpose AISources to check one by oneA traditional GRC toolEvidence often gathered just before the auditRisk HunterEvery conclusion cites its source excerpt, dated and attributed
Follow-upA general-purpose AIThe conversation ends thereA traditional GRC toolAn action plan often tracked in another toolRisk HunterA tracked action plan: owner, deadline, evidence
Your dataA general-purpose AIEntrusted to a general-purpose serviceA traditional GRC toolDepends on the vendorRisk HunterOn-premises and air-gapped if needed, or SaaS hosted in France

“Traditional GRC tool” describes a common market practice, not a specific vendor. Risk Hunter does not replace your scanners or your SIEM: it builds on their results.
Compare for yourself, on your own documents.

Book a demo

Deployment & trust

On your premises or ours. The same product.

Start with one module on a defined scope, then expand without migrating: every module reuses the data already qualified.

In production on-premises, without Internet access, in defence and healthcare.

Exclusive cybersecurity partner of ANCTS.

Founded by a COFRAC technical assessor for ISO 27001 and HDS.

Two patents filed, on exposure and on evidence.

On-premises

Within your perimeter

Data, AI models and decisions stay in your environment, air-gapped if needed.

SaaS

Hosted in France

Hosted in France. Zero Data Retention (ZDR) enabled by default on our AI processing, documents included.

Your model

The AI of your choice

Mistral, Qwen or your in-house model: switch models without switching tools.

Governed AI

We apply to our AI what we audit at your organisation.

Mandatory human approval

No AI proposal is applied without the approval of an authorised person.

Every proposal tracked

What the AI proposed and what a person approved remain separate, dated and attributed.

No training on your data

Your documents are never used to train a model. In SaaS, Zero Data Retention is enabled by default, documents included.

The model of your choice, assessed

Every model undergoes a security assessment before deployment.

An AI governance framework

Aligned with the EU AI Act and ISO/IEC 42001: AI uses, risks and controls documented.

Reproducible results

Same framework, same criteria: every result can be replayed back to its source.

Ecosystem & references

They trust us.

Sectors where mistakes are costly, and a committed French ecosystem.

ANCTS, French national association of local-government security officers

Partnership

Exclusive cybersecurity partner of ANCTS

Risk Hunter supports ANCTS, the French national association of local-government security officers, across the full security continuum: from cybersecurity to the physical security of buildings and public spaces, alongside local authorities and public safety stakeholders.

Our references

DefenceHealthcareCritical infrastructureInsurance & reinsuranceIndustryTransport

Technologies & partners

Ecosystem

FAQ

Answers before you book.

Which frameworks does Risk Hunter cover?

EBIOS RM, ISO 27001 and ISO 27005, NIS2, DORA, HDS, the Cyber Resilience Act (CRA), the EU AI Act, IGI 1300 and II 901, as well as the MITRE ATT&CK and MITRE ATLAS attack frameworks. You can also load your own audit templates.

Can you run the analysis or audit with us?

Yes. Our experts can deliver the engagement with Risk Hunter on your scope, then hand over the deliverables and the platform.

How long does it take to get started?

On a first module and a defined scope, your first priorities come out within minutes from your data. On-premises deployment is scoped with your technical team.

Does the AI make decisions for us?

No. The AI prepares the analyses and proposes treatments. Approvals and trade-offs remain the responsibility of authorised people, and are tracked.

Does the platform work without Internet access?

Yes, in an air-gapped on-premises deployment. It is already running in production in defence and healthcare.

Can we start with compliance?

Yes. The Audit & Compliance module works on its own; the others can be added later on the same data.

Does Risk Hunter replace our security tools?

No. It builds on the output of your scanners, inventories and documents to derive risks, priorities and evidence.

Your next audit, your next accreditation, prepared with Risk Hunter.

A demo on a use case from your sector, then an assessment on your own data, under an approved framework.

* Required fields. Your details are sent to Risk Hunter so we can respond to your request. Privacy

Book a demo